From Ars Technica · · 1m 40s
Claude Code leaking secrets on GitHub
Anthropic's Claude Code is exposing thousands of database passwords, API tokens and private keys in public repositories through misconfigured settings files.
In brief
Anthropic's Claude Code is exposing thousands of database passwords, API tokens and private keys in public repositories through misconfigured settings files. Claude Code settings files containing sensitive information are being accidentally uploaded to public GitHub repositories, exposing thousands of secrets from…
Claude Code leaking secrets
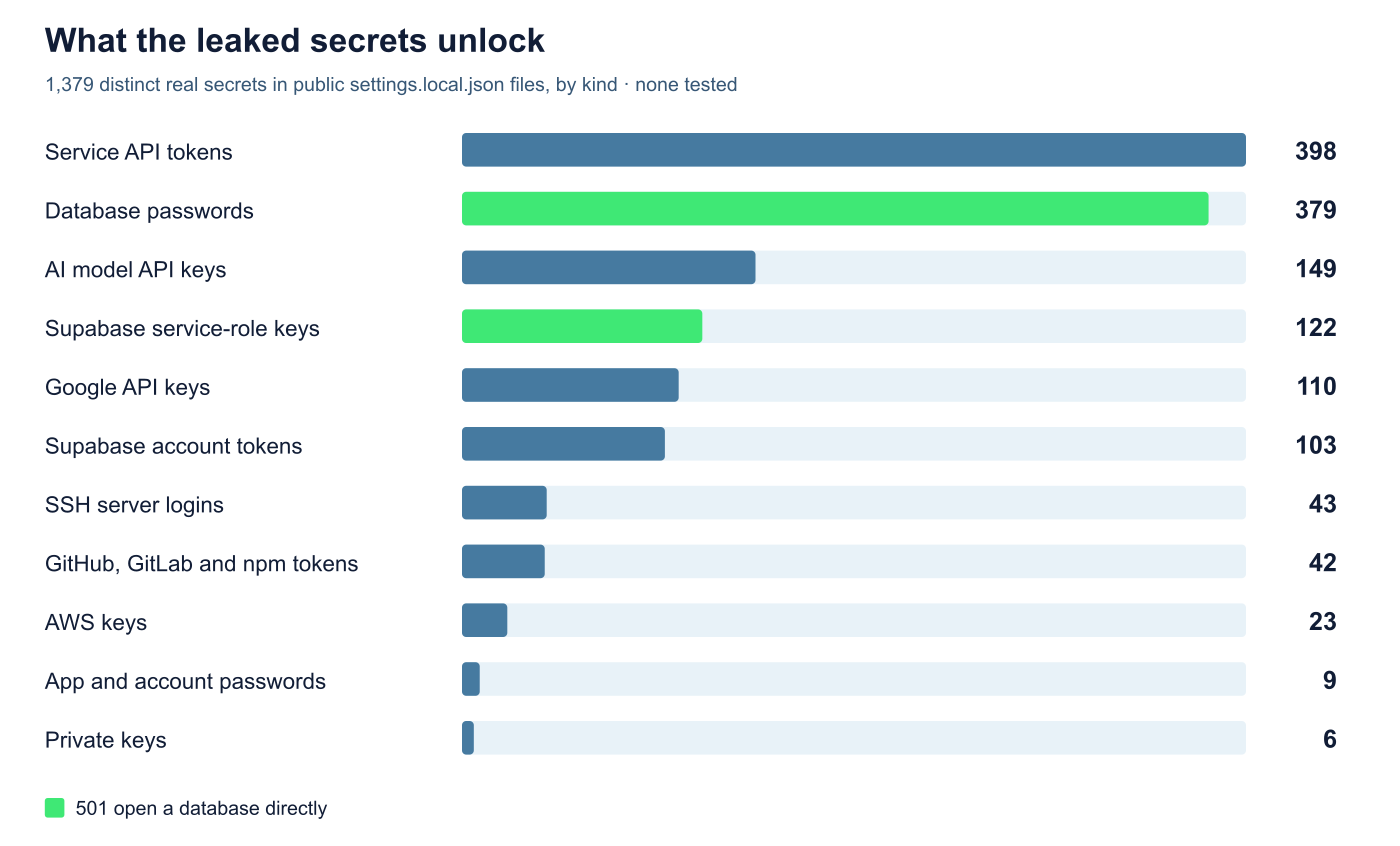
AI security researchers at Apiiro discovered thousands of secrets including database passwords, API tokens and root logins in Claude Code settings files embedded in GitHub repositories.
How the leak happens
When users approve running commands with "Yes, and don't ask again", Claude Code stores that choice in a local .claude/settings.local.json file, often including sensitive information embedded in the command itself.
The gitignore gap

Anthropic adds the settings file to the global .gitignore list, but not at the repository level.
Scale of the problem
Apiiro's researchers found over one hundred thousand cases where Claude Code's local settings file had been uploaded to a public GitHub repository. About one thousand one hundred from sixty three different organizations contained secrets.
Bug reports ignored
The issue was flagged in a Claude Code bug report as far back as August twenty twenty five. Multiple bug reports were closed without action after sixty days of inactivity.
Anthropic's response
Claude Code's Boris Cherny said the team is "looking into what we can do to prevent this".
“looking into what we can do to prevent this”
Secret scanners miss many leaks
Apiiro researchers found that two hundred fifteen of the roughly one thousand one hundred public secrets in Claude Code settings files were not flagged by popular secret scanners gitleaks and TruffleHog.
Here's the gist
Claude Code settings files containing sensitive information are being accidentally uploaded to public GitHub repositories, exposing thousands of secrets from dozens of organizations.