From Ars Technica · · 1m 30s
Google shuts down botnet on 1.3 million Android TV boxes
Google's Threat Intelligence Group dismantled x.cpe, a malware operation that infected certified Android TV devices from manufacturer Videostrong, mostly sold under the MECOOL brand.
In brief
Google's Threat Intelligence Group dismantled x.cpe, a malware operation that infected certified Android TV devices from manufacturer Videostrong, mostly sold under the MECOOL brand. Google shut down a botnet running on 1.3 million certified Android TV boxes made by Videostrong, which used obfuscation to evade…
Botnet found on certified devices
Google's Threat Intelligence Group shut down x.cpe, a botnet running on more than 1.3 million Android TV devices. The boxes were Google-certified, made by Shenzhen-based Videostrong Technology, mostly sold under the MECOOL brand.
How the malware evaded detection
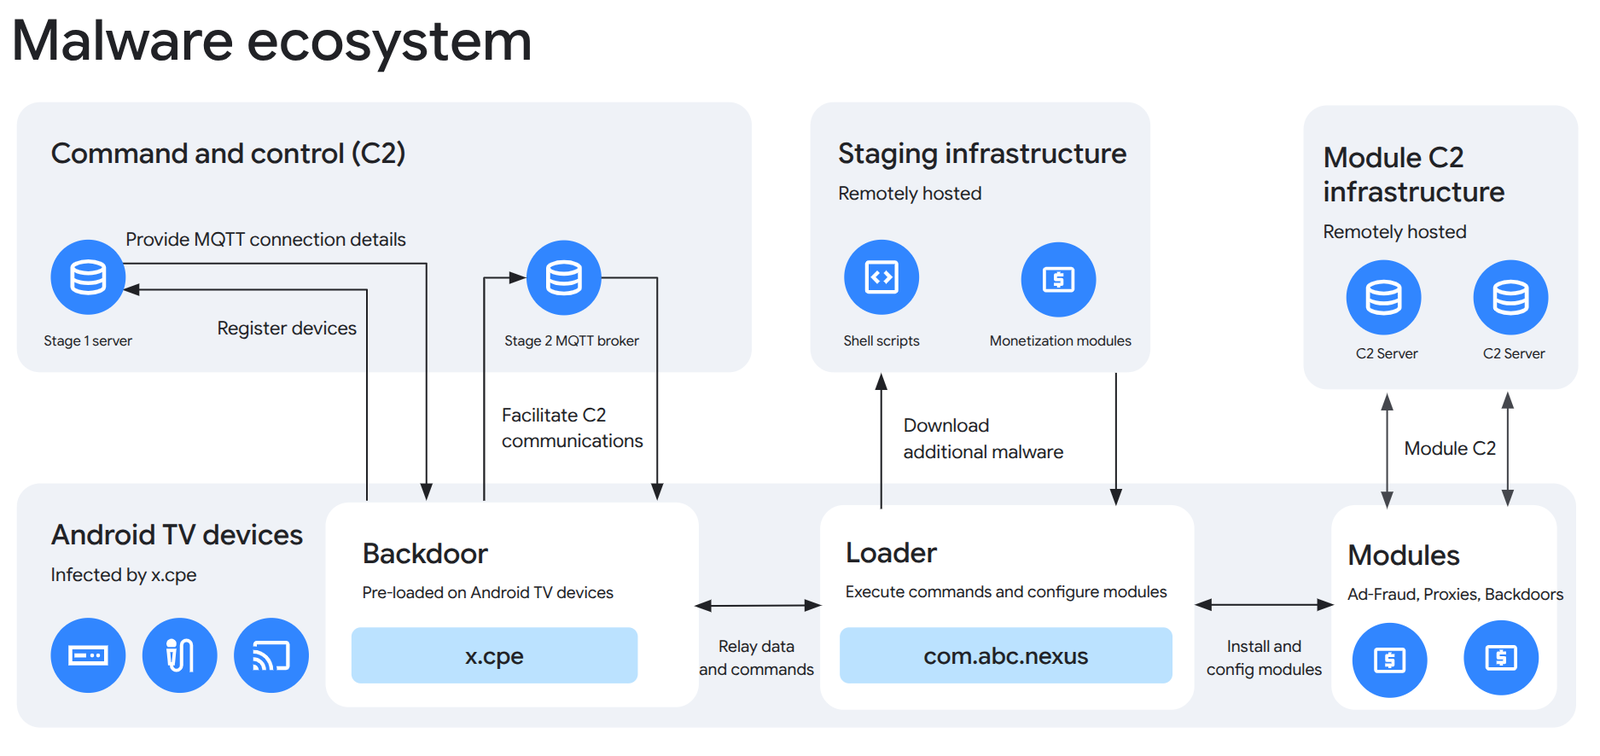
Videostrong used obfuscation techniques to bypass Google's screening process. A stub application called x.cpe or com.oemservice installed malware after devices went online, disabling Play Protect to hide silently installed packages.
What the botnet did

Most infected boxes ran residential proxies routing nefarious traffic or modules engaging in ad fraud. Videostrong had full device access, allowing operators to run terminal commands, capture screens, and probe other devices on local networks.
Google's takedown operation
Google worked with Japan's National Police Agency, Synthient, and Trend Micro to disrupt the network.
Where the infected devices were
Trend Micro counted 1,472,554 infected devices. The overwhelming majority were in Brazil, Malaysia, Iraq, Mexico, and Taiwan, but tens of thousands were also online in the US, Germany, the UK, Australia, and Canada.
Google bans Videostrong and updates process
Google ended its relationship with Videostrong and banned the company and subsidiaries from using Android apps and services.
The big picture
Google shut down a botnet running on 1.3 million certified Android TV boxes made by Videostrong, which used obfuscation to evade screening and sold access to third parties.