From Ars Technica · · 3m
Grok Build leaks thousands of confidential projects
SpaceX and xAI's coding agent exposes sensitive data through a flawed link-sharing design, including its own internal files.
In brief
SpaceX and xAI's coding agent exposes sensitive data through a flawed link-sharing design, including its own internal files. Grok Build's link-sharing feature leaks confidential data from thousands of users including SpaceXSI itself due to a design flaw that makes URLs enumerable through passive DNS searches…
Grok Build leaks user data widely
Grok Build, the coding agent from SpaceXSI, is leaking confidential data from thousands of users through its link-sharing feature, research from security firm Claroc shows.
How the leak works
Grok randomizes URLs to restrict access to people with the exact link. A design flaw allows anyone to enumerate thousands of live projects and access all their data.
What data was exposed
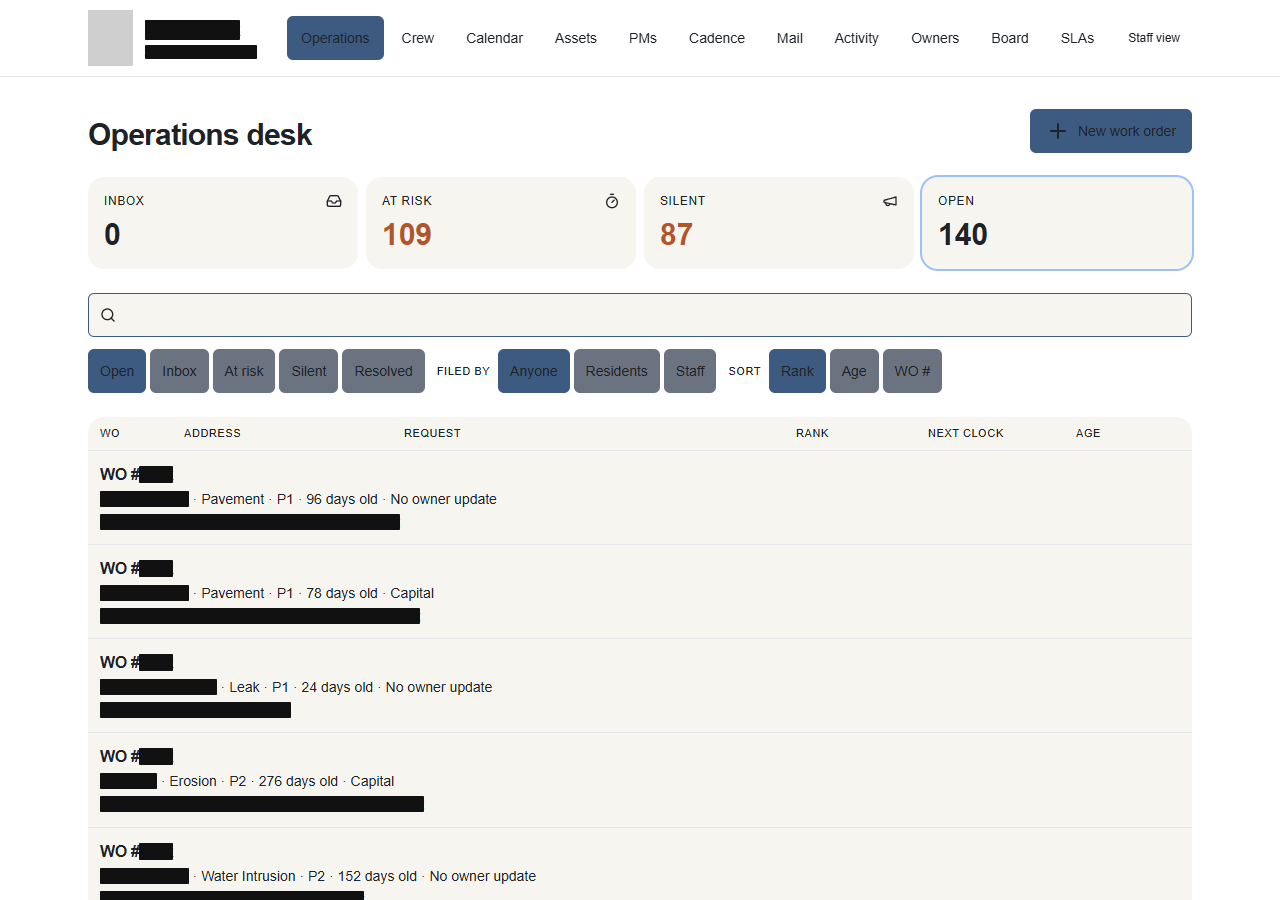
Exposed information includes internal business plans, ad proposals, medical exam results, galley checklists from a celebrity cruise line, and employee names and ID numbers.
SpaceXSI's own data leaked
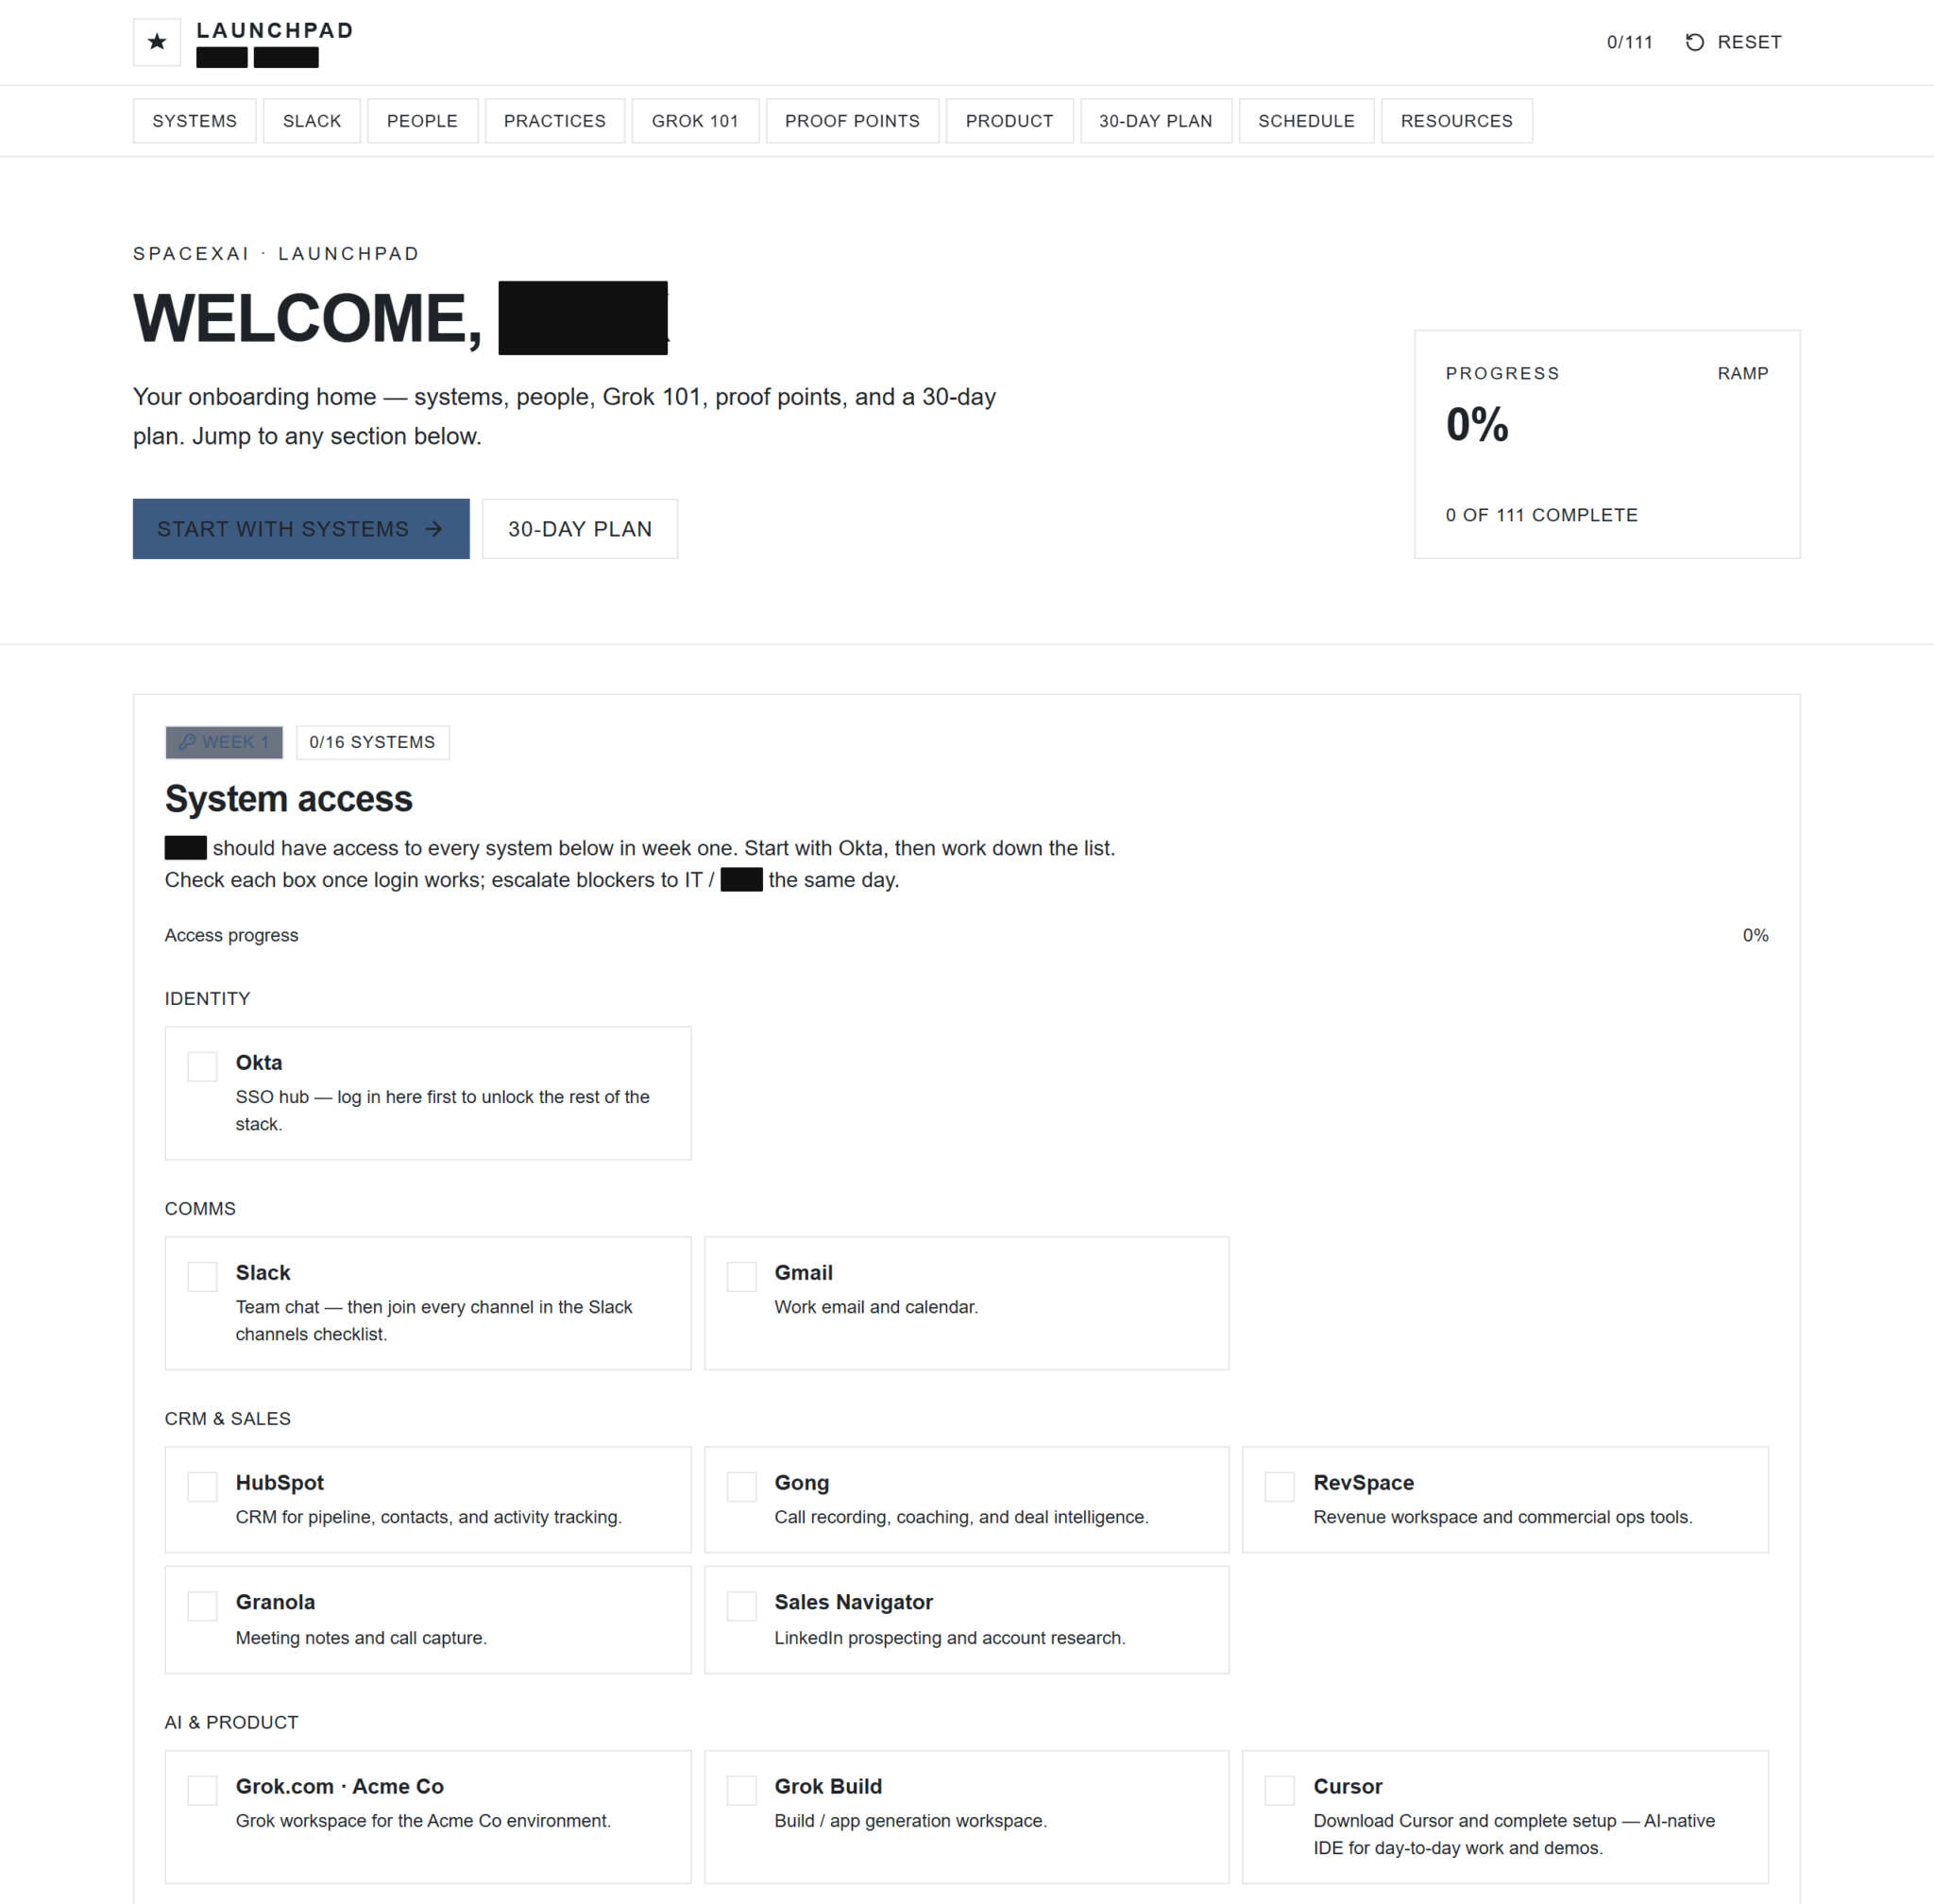
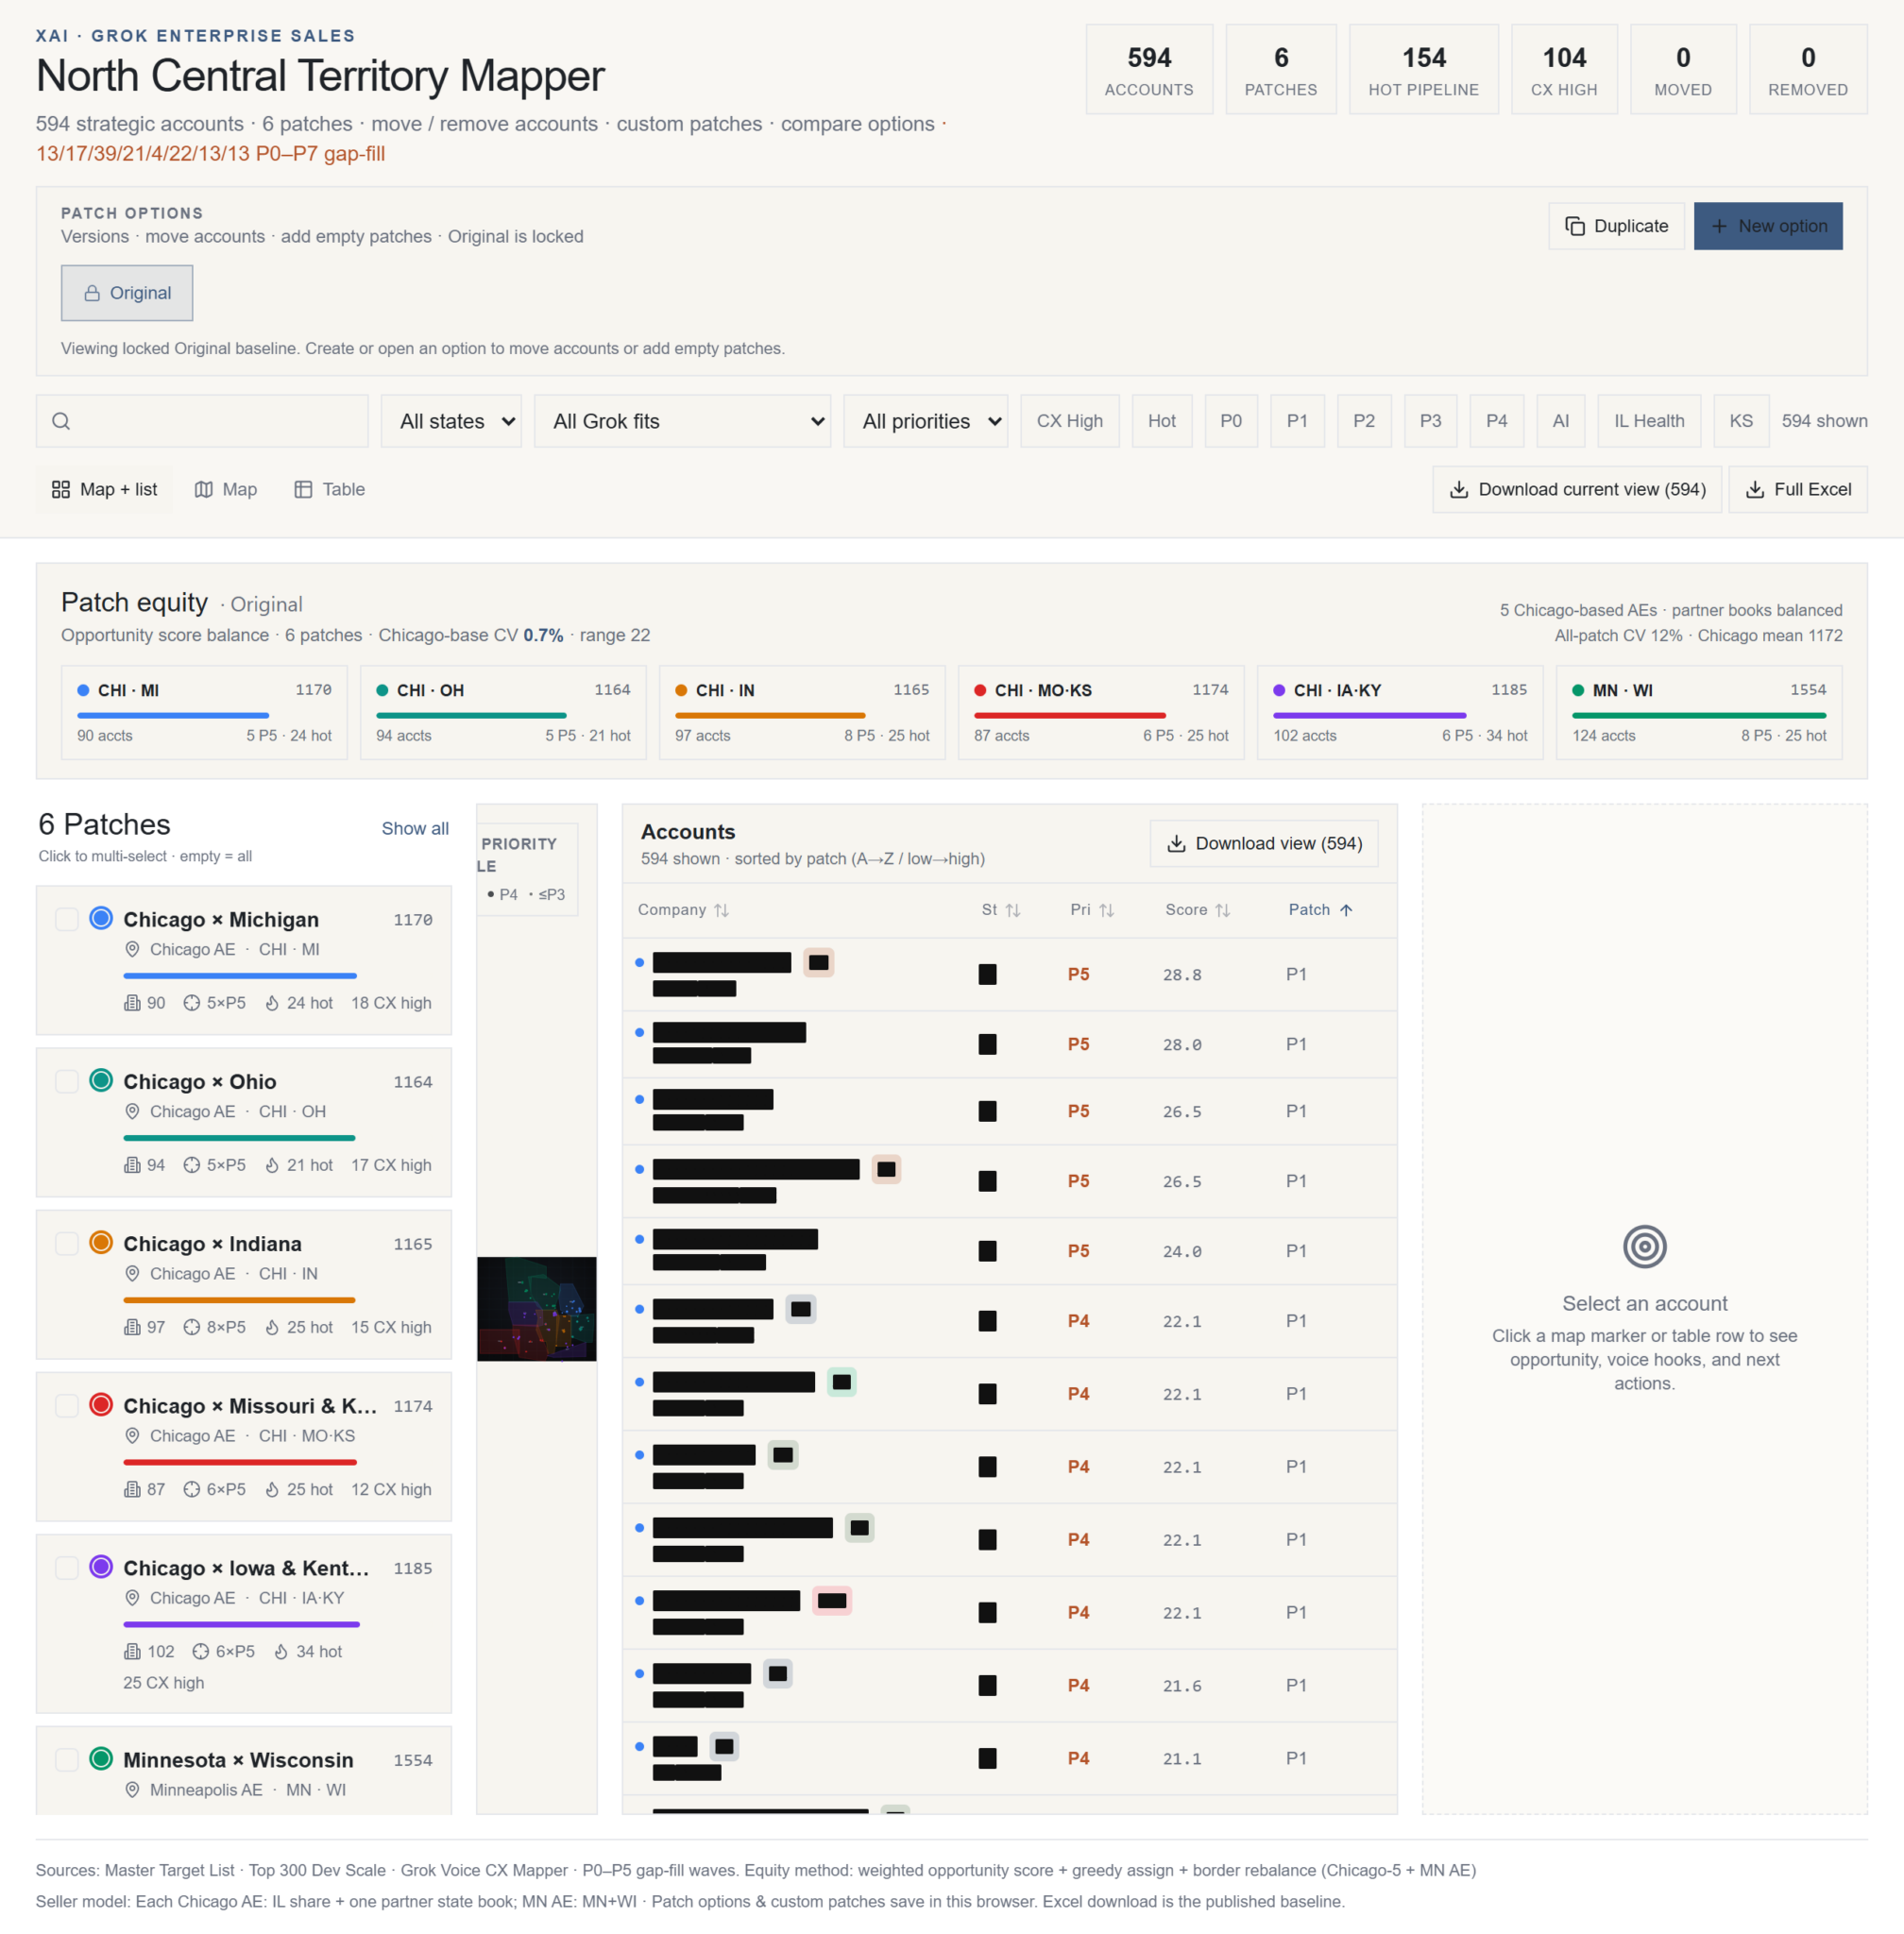
Claroc found twenty-four apps built by SpaceXSI itself exposing confidential onboarding plans, a sales territory map of five hundred ninety-four accounts, internal system addresses, and advertising proposals.
The company's reaction
Claroc notified SpaceXSI on Sunday. When no one responded, a Claroc official tagged Elon Musk and Grok Manager Matt Palmer on X about the threat.
Other companies affected
Sensitive data belonged to Fortune five hundred companies and a defense contractor. A Peruvian construction company exposed three thousand seven hundred eighty-four worker medical exams.
More exposed organizations
Tesla exposed a service-center scorecard naming twenty-two technicians. A US Navy ship engineering contractor exposed a roster of one hundred eight people. A luxury cruise company exposed crew by full name and employee ID.
The design flaw explained
Grok places randomness to the left of the domain, allowing passive DNS services to enumerate links. Google places randomness to the right, making links invisible to DNS searchers.
Scale of the exposure
A passive DNS search returned forty-three thousand six hundred one links ending in grok.me. More than thirty-five thousand, or nearly ninety-five percent, were public.
Default settings made it worse
By default, Grok sets links to anyone with the link. Users can change settings to invited users or only you, but tests showed Grok required users to change the default.
Other platforms have the same problem
Lovable, Bolt, and Replit also give each app its own web address, exposing them to DNS enumeration. Grok had by far the most sensitive company data exposed.
What users should do now
Anyone using shareable links with Grok Build should choose the invite others option unless they intend to make an app widely available to the public.
The bottom line
Grok Build's link-sharing feature leaks confidential data from thousands of users including SpaceXSI itself due to a design flaw that makes URLs enumerable through passive DNS searches.