From Kaba · · 1m 10s
How I got over 300 Tor exit nodes removed
333 infected Tor exit nodes shut down after SSH attack.
In brief
333 infected Tor exit nodes shut down after SSH attack. 333 infected Tor exit nodes were shut down after attackers intercepted SSH connections and stole credentials. Originally reported by Kaba.
Attack starts
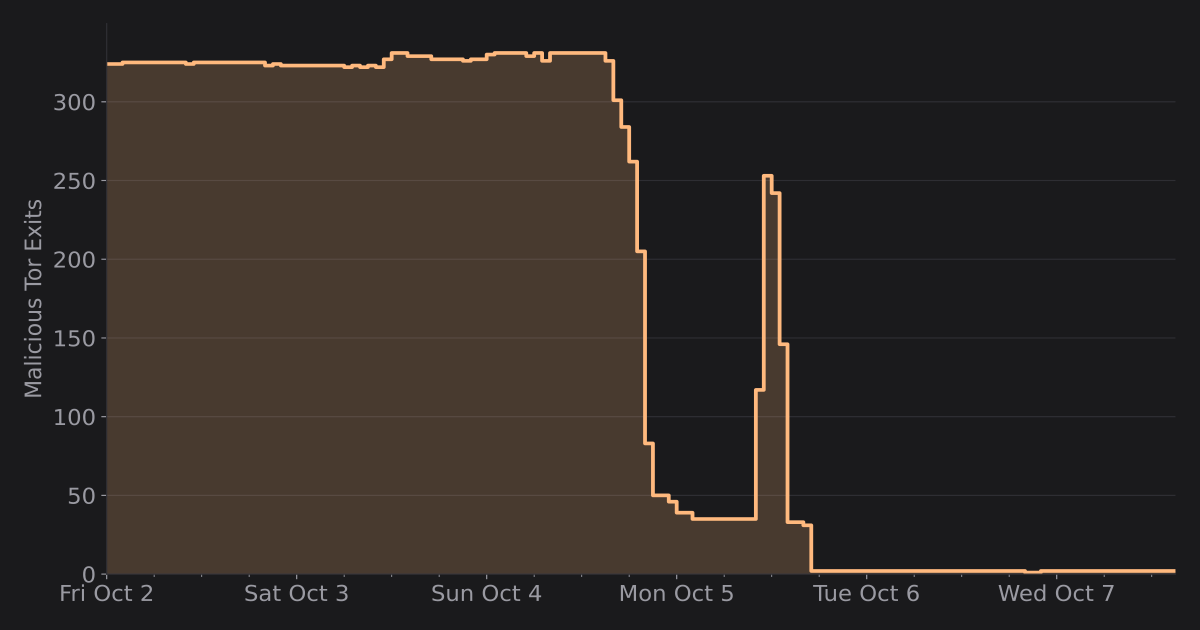
On Friday Oct 2, 2026, 333 infected Tor exit nodes started intercepting SSH connections.
Scale of attack
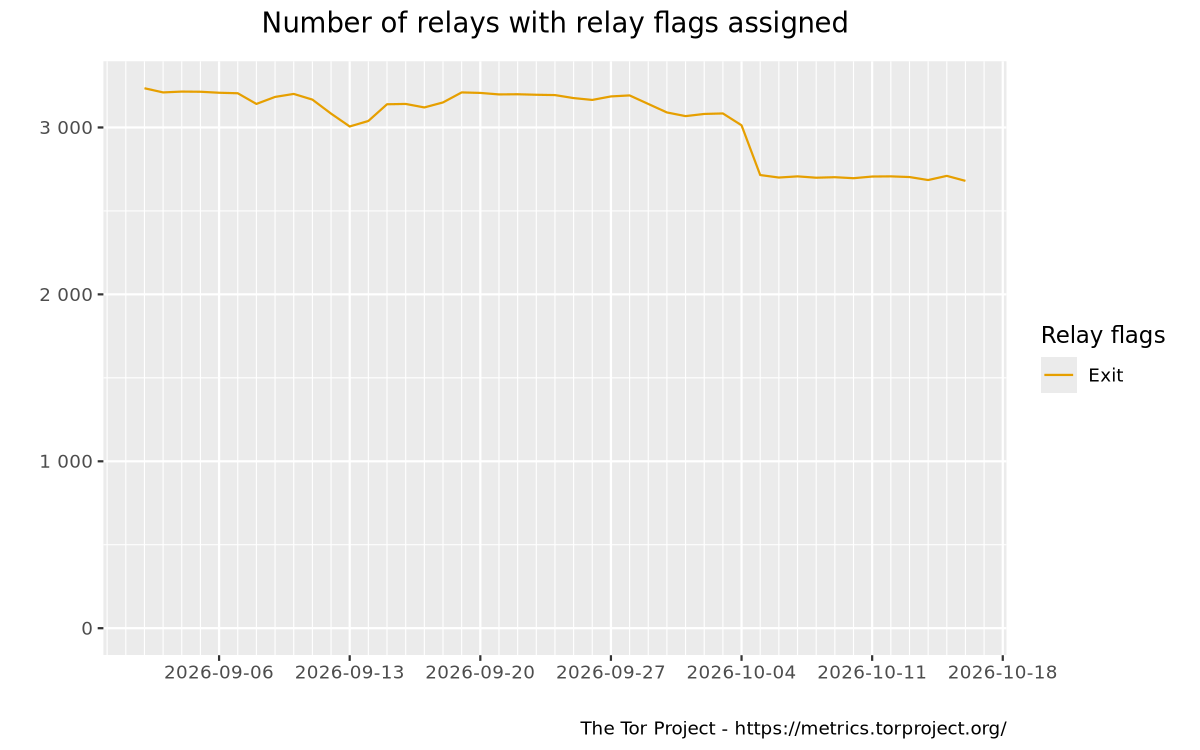
All of Tor has around 3000 exit relays, so roughly 10% were under their control.
How they gained access
The attackers gained access two months earlier in August and deployed Ebury 1.8.3 payload.
SSH interception method
Infected nodes block ports to handle only unencrypted mail traffic and redirect SSH connections.
My SSH connection
My SSH connection got redirected to an interception server with a warning about host identification change.
What attackers do
Attackers steal passwords, observe commands, and infect servers with Ebury.
Response timeline
Tor health team contacted operators on Friday evening, marking nodes as BadExit by Sunday.
Nodes shut down
All infected servers were shut down by Monday, with some relays remaining as middle relays.
Technical details
I used exitmap to find infected nodes by checking SSH fingerprints and redirection patterns.
The key point
333 infected Tor exit nodes were shut down after attackers intercepted SSH connections and stole credentials.