Maersk’s Legacy System Breach Highlights M&A Cyber Risks
Maersk’s legacy system breach reveals critical cyber gaps in mergers and acquisitions.
In brief
Maersk’s legacy system breach reveals critical cyber gaps in mergers and acquisitions. Maersk’s legacy system breach shows M&A’s need for stronger cyber security post-acquisition. Originally reported by Pymnts.
Maersk Discloses Legacy System Breach
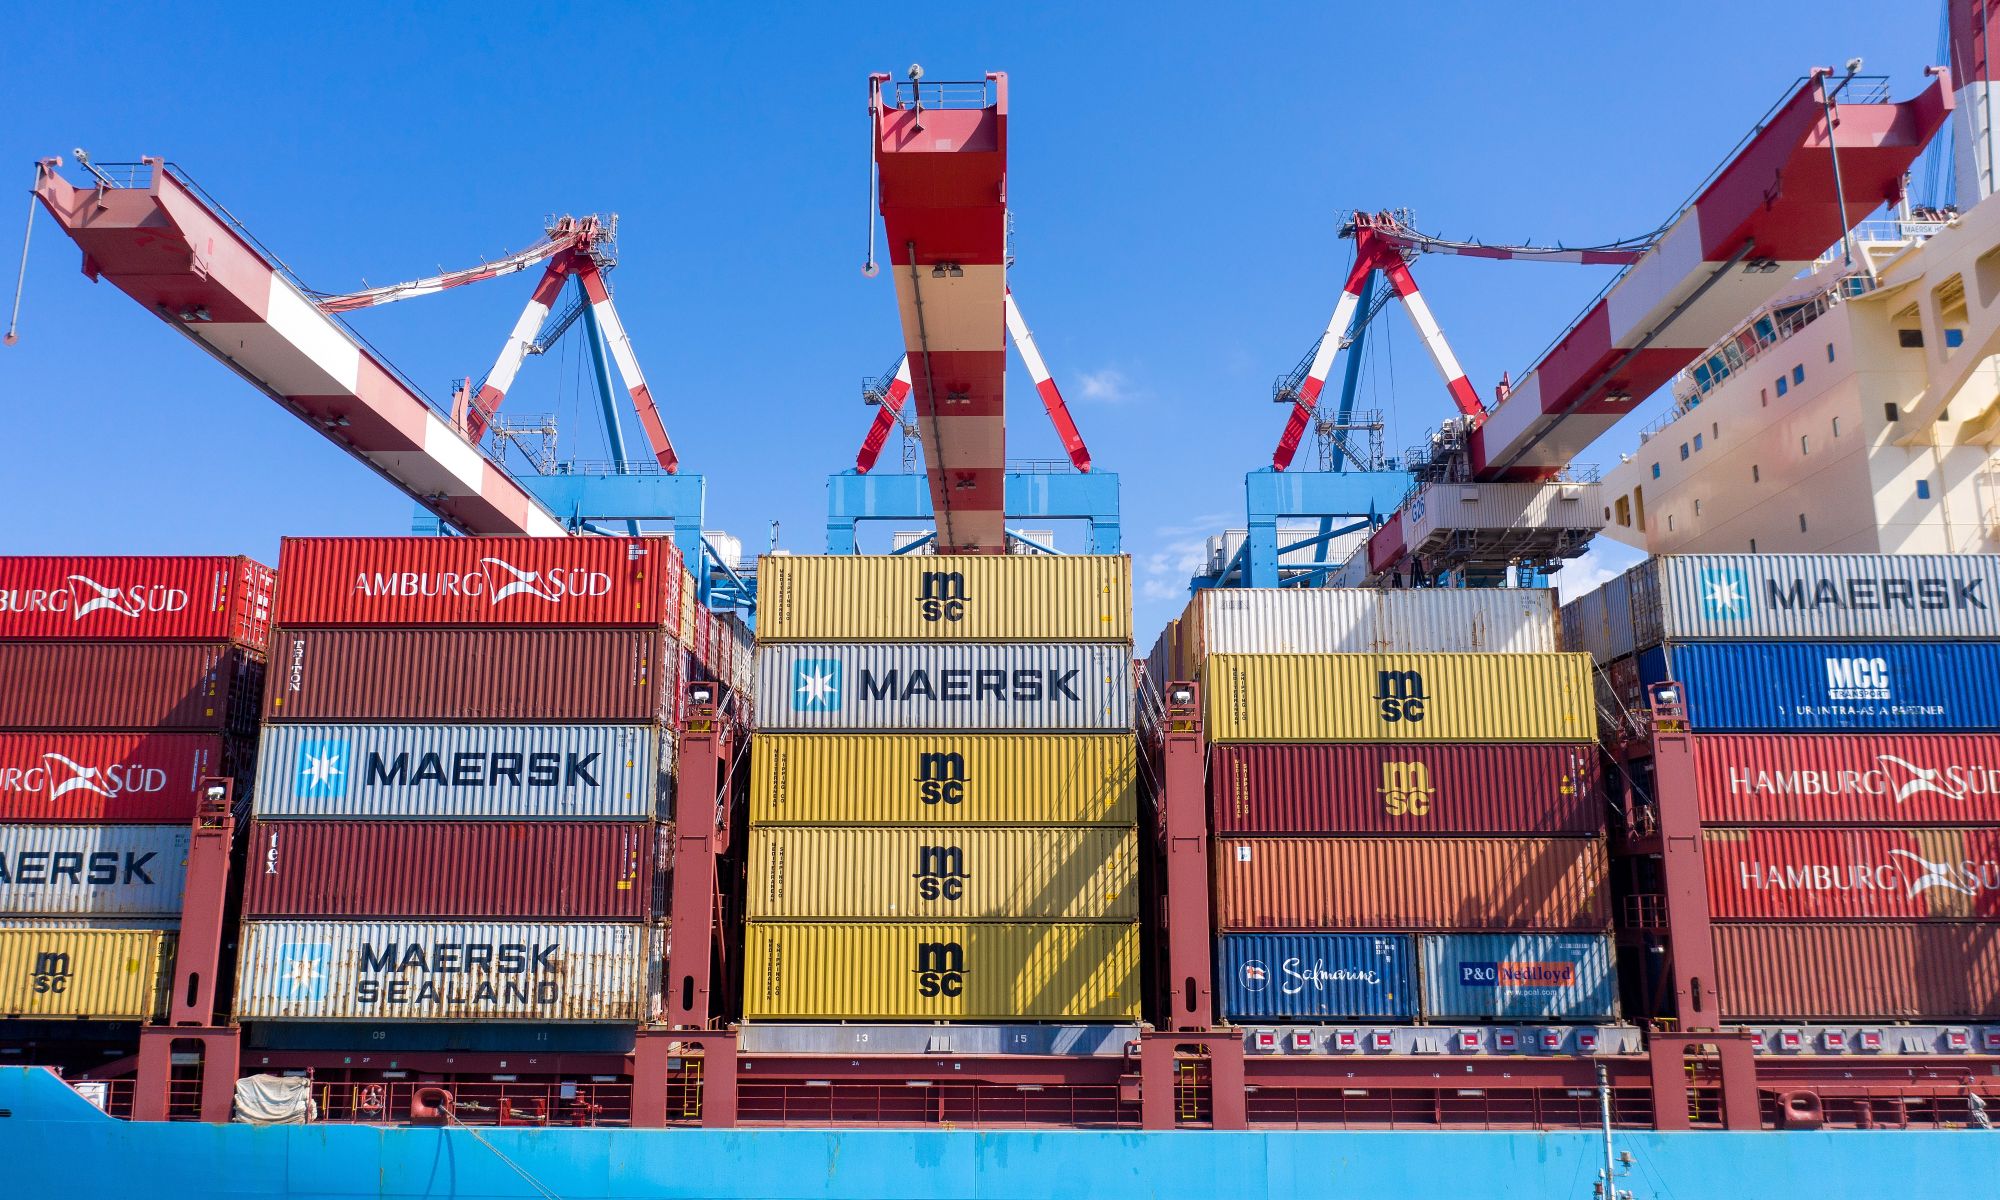
Shipping giant A.P. Moller-Maersk disclosed Wednesday (Nov. 11) that an unauthorized party accessed and extracted data from a legacy IT system inherited through a previous acquisition.
No Companywide Compromise Reported
Maersk has not reported a companywide compromise, but the incident illustrates a persistent problem for acquisitive businesses.
Inherited Systems Pose Long-Term Risks
Technology inherited through M&A can remain an operational and security obligation long after the transaction’s financial benefits have been incorporated into performance expectations.
Investigation Ongoing with No Data Exposure
The company said its investigation remains ongoing, with preliminary findings suggesting no sensitive data was disclosed and no indication of disruption to its broader operations or connected customer systems.
In short
Maersk’s legacy system breach shows M&A’s need for stronger cyber security post-acquisition.