From RuntimeWire · RuntimeWire · · 40s
Cloudflare WAF checks attack success before blocking
Cloudflare's new security rules check if an attack worked before blocking responses.
In brief
Cloudflare's new security rules check if an attack worked before blocking responses. Cloudflare updated its web application firewall to detect successful exploits by checking application responses after suspicious requests. Originally reported by RuntimeWire.
Cloudflare updates security rules
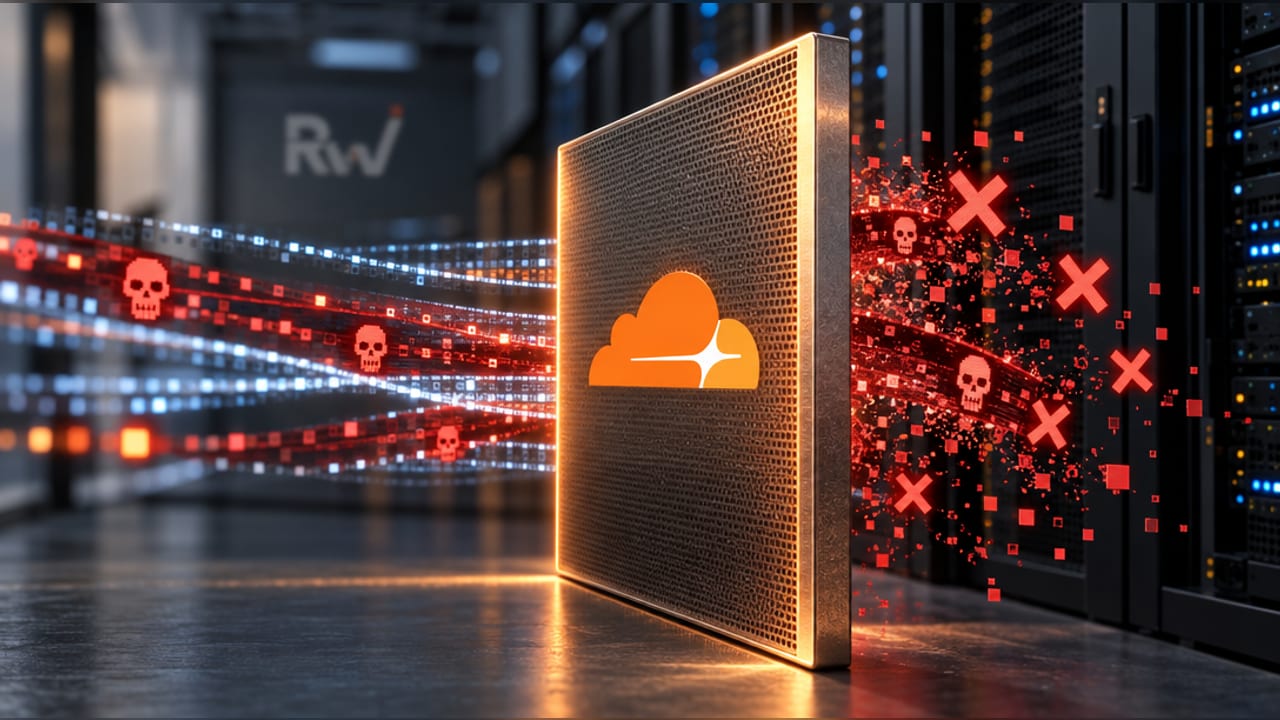
Cloudflare's web application firewall now checks application responses after suspicious requests to identify successful exploits.
New capabilities announced
Cloudflare announced full-transaction detection and response rules on October 21st to stop origin replies from reaching requesters.
Why it matters
This helps security teams gather evidence for blocking exploits while keeping software patching essential.
What to remember
Cloudflare updated its web application firewall to detect successful exploits by checking application responses after suspicious requests.