From TechRadar · · 2m
TP-Link camera flaws let hackers spy on your home
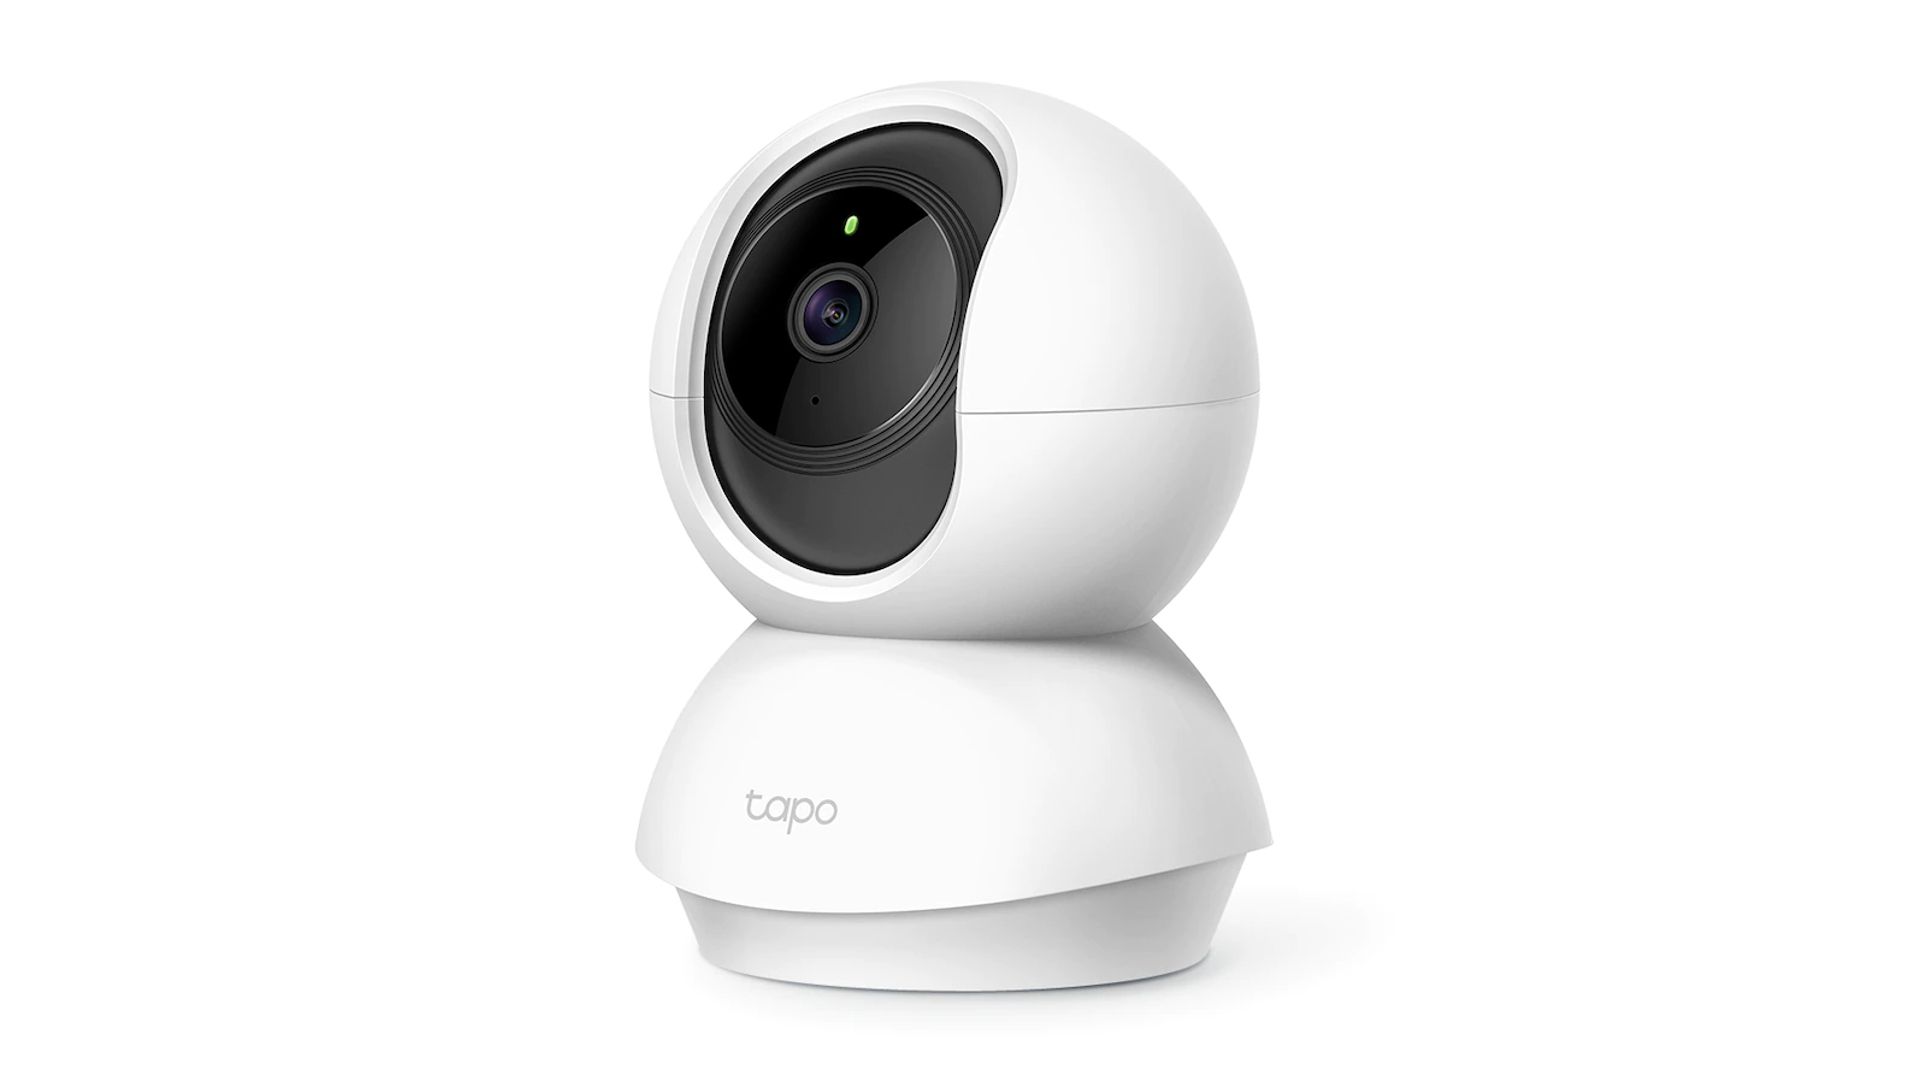
Two critical vulnerabilities in popular Tapo C200 cameras could expose millions of users to unauthorized access and device crashes.
In brief
Two critical vulnerabilities in popular Tapo C200 cameras could expose millions of users to unauthorized access and device crashes. Update your TP-Link Tapo C200 camera to firmware V5_1.4.6 immediately to patch authentication bypass and denial-of-service flaws. Originally reported by TechRadar.
Two critical camera flaws discovered
Opswat found authentication bypass and denial-of-service vulnerabilities in TP-Link Tapo C200 smart cameras. The auth bypass lets attackers gain admin access without a password.
Auth bypass lets attackers watch streams
The CVE-2026-15315 flaw allows unauthenticated attackers to obtain valid admin sessions without passwords, letting them manage devices and watch live video feeds.
Denial-of-service crashes devices
The CVE-2026-15316 flaw lets attackers send oversized encrypted values that crash cameras or restart them, disrupting HTTPS management and monitoring until the service recovers.
Millions of users potentially exposed
The Tapo app has over 13 million users with 10+ million Google Play Store downloads. The C200 is Amazon's top-rated camera in its category with 3,000+ purchases this month.
TP-Link released patch in August
TP-Link released firmware version V5_1.4.6 on August 18, 2026, addressing both flaws. Users are advised to install the update as soon as possible.
Camera features make it popular
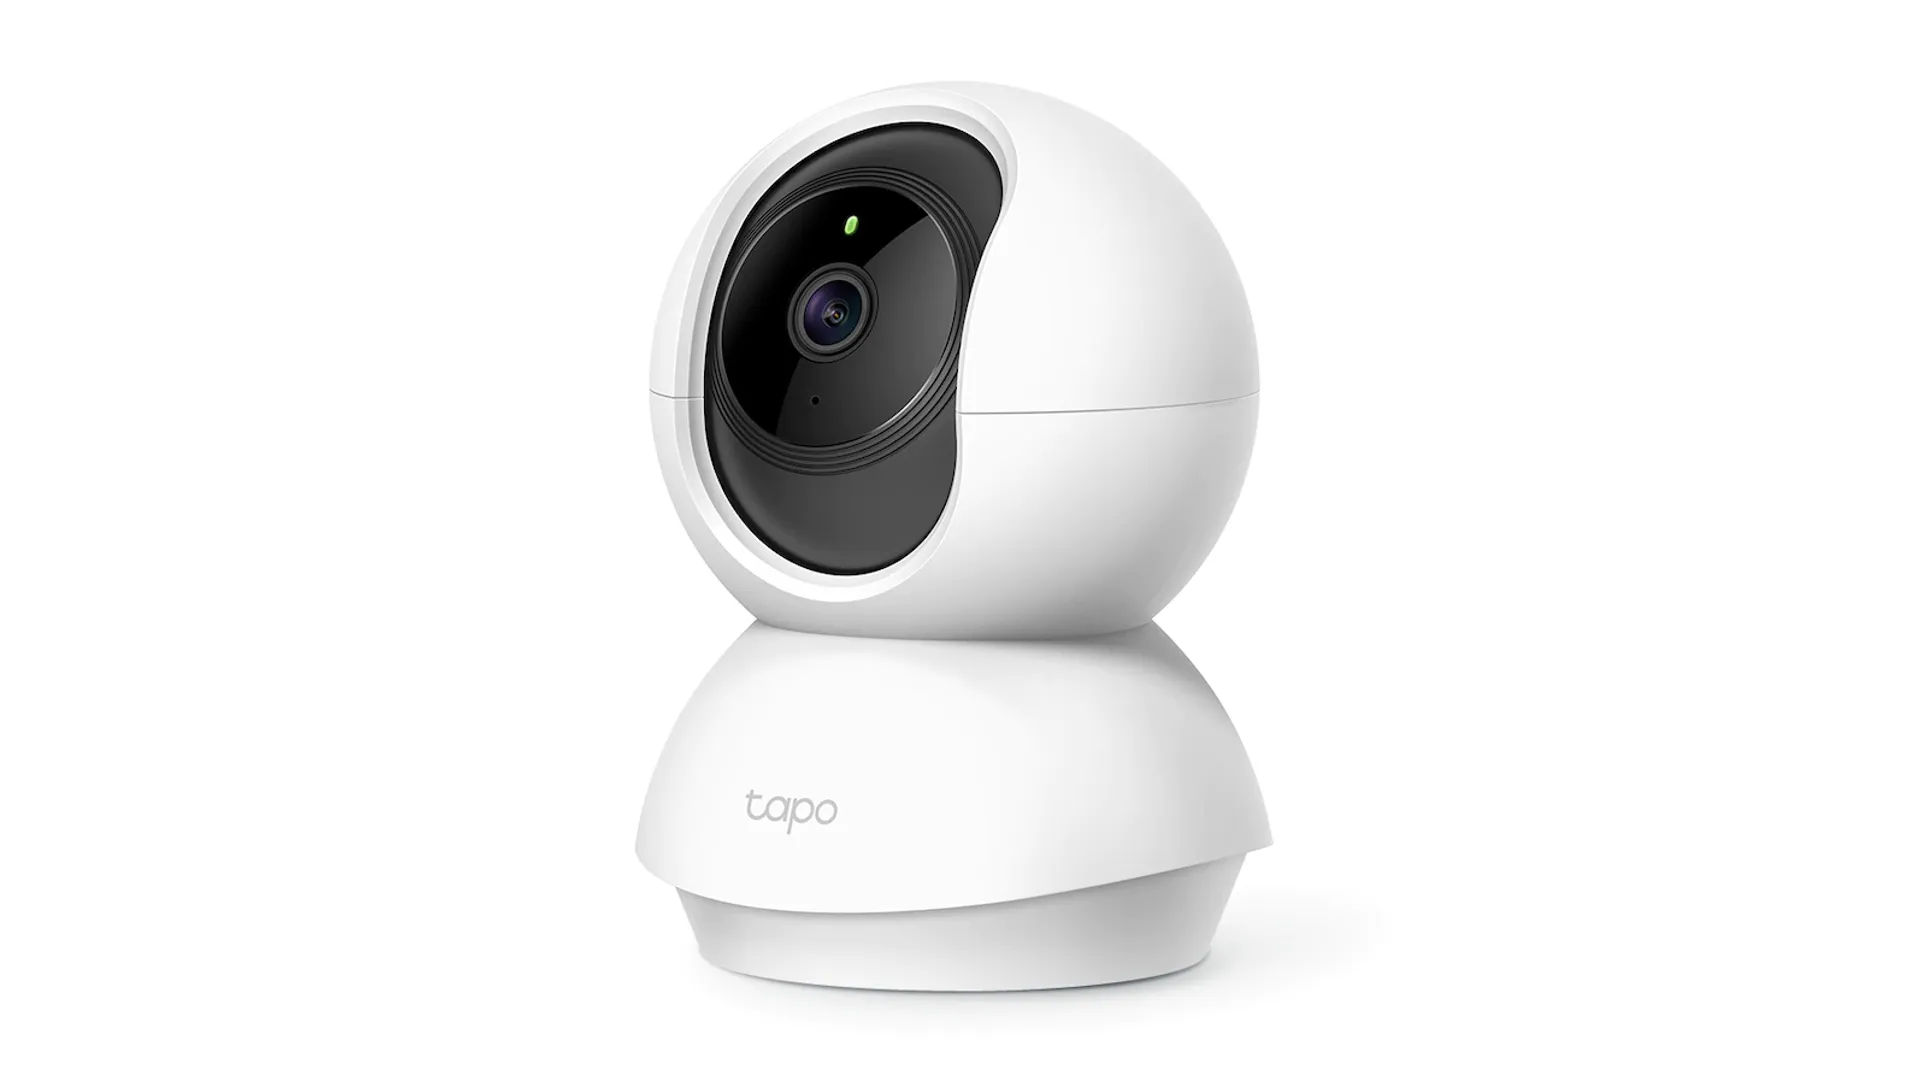
The C200 offers 1080p video, 2-way audio, night vision, motion detection, cloud and SD card storage, plus Alexa and Google Home integration. It's marketed as a security camera, baby monitor, or pet camera.
Local network access required for exploit
Security expert Dahvid Schloss notes the exploit requires local network access, meaning attackers must be on your Wi-Fi or control a device already on your network.
“running this exploit requires local network access, so a threat actor has to be on your Wi-Fi or already own a device that is.”
Port-forwarding creates bigger risk
If your camera is port-forwarded to the internet, it becomes a bigger security concern. However, this is not a common setup for everyday home users.
Still patch your camera anyway
Despite the lower risk for typical home setups, security experts recommend patching the camera immediately. It's a straightforward way to eliminate the vulnerability entirely.
“I'd still patch the camera, but it's pretty low on the totem pole of what a cybercriminal wants.”
What it means
Update your TP-Link Tapo C200 camera to firmware V5_1.4.6 immediately to patch authentication bypass and denial-of-service flaws.





