From koreajoongangdaily · News Team · · 1m 50s
Korea raises data breach fines to 10% of revenue
South Korea's privacy regulator is sharply raising penalties for major data leaks, aiming to make companies treat data protection as a preventive investment rather than a routine cost.
In brief
South Korea's privacy regulator is sharply raising penalties for major data leaks, aiming to make companies treat data protection as a preventive investment rather than a routine cost. Companies that leak 10 million or more people's data through intent or gross negligence now face fines up to 10 percent of annual…
Korea tightens data breach penalties
Starting September 12, 2026, companies that leak 10 million or more people's personal data through intent or gross negligence face fines up to 10 percent of annual revenue, up from 3 percent.
Real impact: Coupang's case
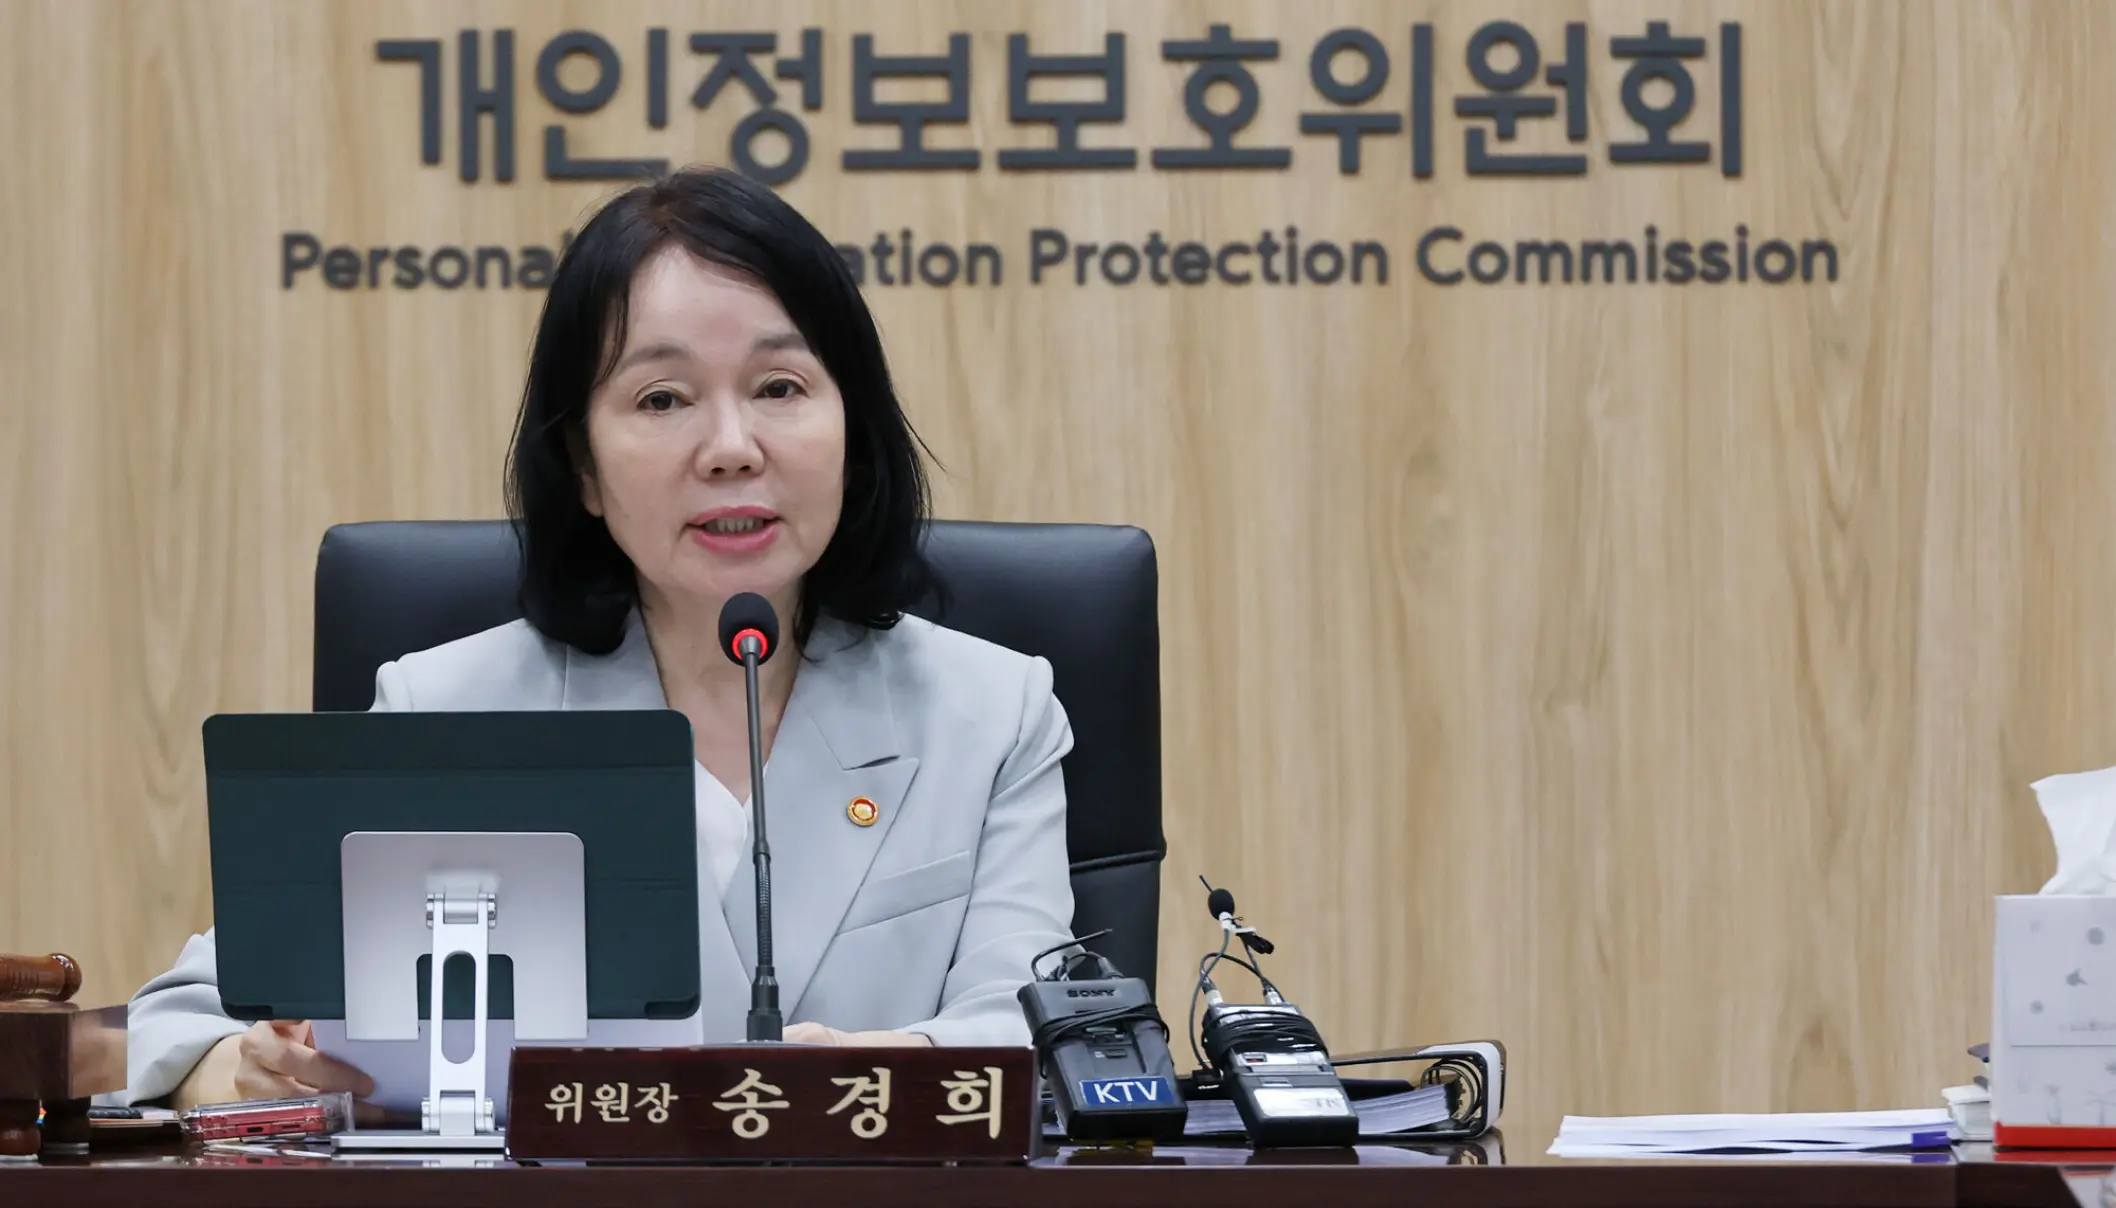
E-commerce giant Coupang was fined 624.6 billion won in June 2026 for leaking 37.55 million people's data. Under the new standard, that fine could reach trillions of won.
72-hour breach notification required
Companies must now notify users within 72 hours if there is a high likelihood their personal data was exposed, even if a breach hasn't been confirmed yet.
“Even if a leak hasn't been confirmed, companies must notify users within 72 hours if the risk of exposure is high.”
Investment in protection gets rewarded
Companies that invested in data protection beforehand can receive up to 40 percent fine reductions. Early detection and prompt reporting can also cut fines by up to 40 percent.
Chief privacy officers gain power
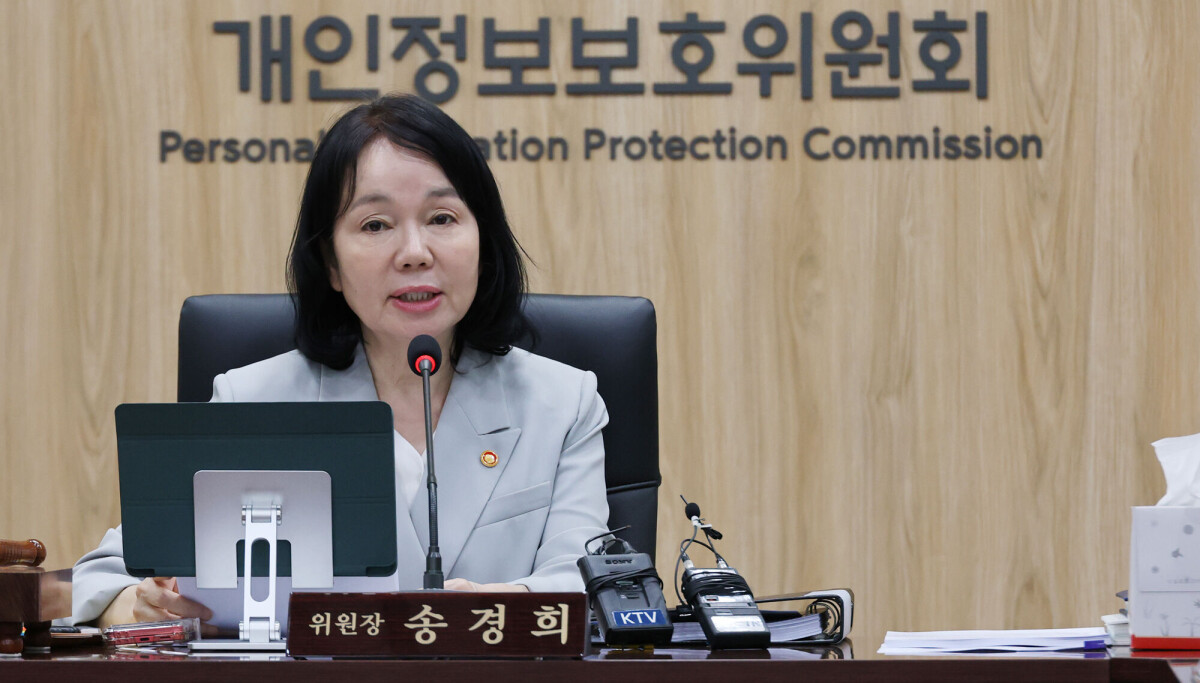
Large companies and institutions must now get board approval before appointing, changing or dismissing a chief privacy officer and report the decision to regulators.
Who must comply with new rules
Companies with annual revenue exceeding 180 billion won that process 1 million or more people's data, plus universities with 20,000 students and major hospitals, fall under the stricter requirements.
Shifting from cost to investment
The regulator expects companies to view data protection spending as a proactive investment that builds customer trust and expands profit, rather than just a cost of doing business.
“We expect the way companies view investment in data protection to shift from seeing it as a cost to treating it as a proactive investment that builds customer trust and expands corporate profit.”
Here's the gist
Companies that leak 10 million or more people's data through intent or gross negligence now face fines up to 10 percent of annual revenue, up from 3 percent previously.