#prompt injection
6 stories

AI agents have a hidden security flaw
Vulnerabilities in how AI agents communicate with each other let attackers hijack one agent to control others, exposing sensitive data across organizations.
Ars Technica · 2m

AI Prompt Security: Why Stopping All Exploits Is Impossible
AI security can't stop every prompt attack, experts say.
PCMAG · 1m

Meta's Muse AI leaks its own secrets
Developers easily coaxed Meta's new AI into sharing its entire filesystem, revealing how it works and raising questions about its security.
The Verge · 1m
AI watermarks may weaken the safeguards they're meant to protect
Research shows that adding watermarks to prove text is AI-generated can unintentionally make language models more willing to answer harmful requests.
TechRadar · 1m · 5 views
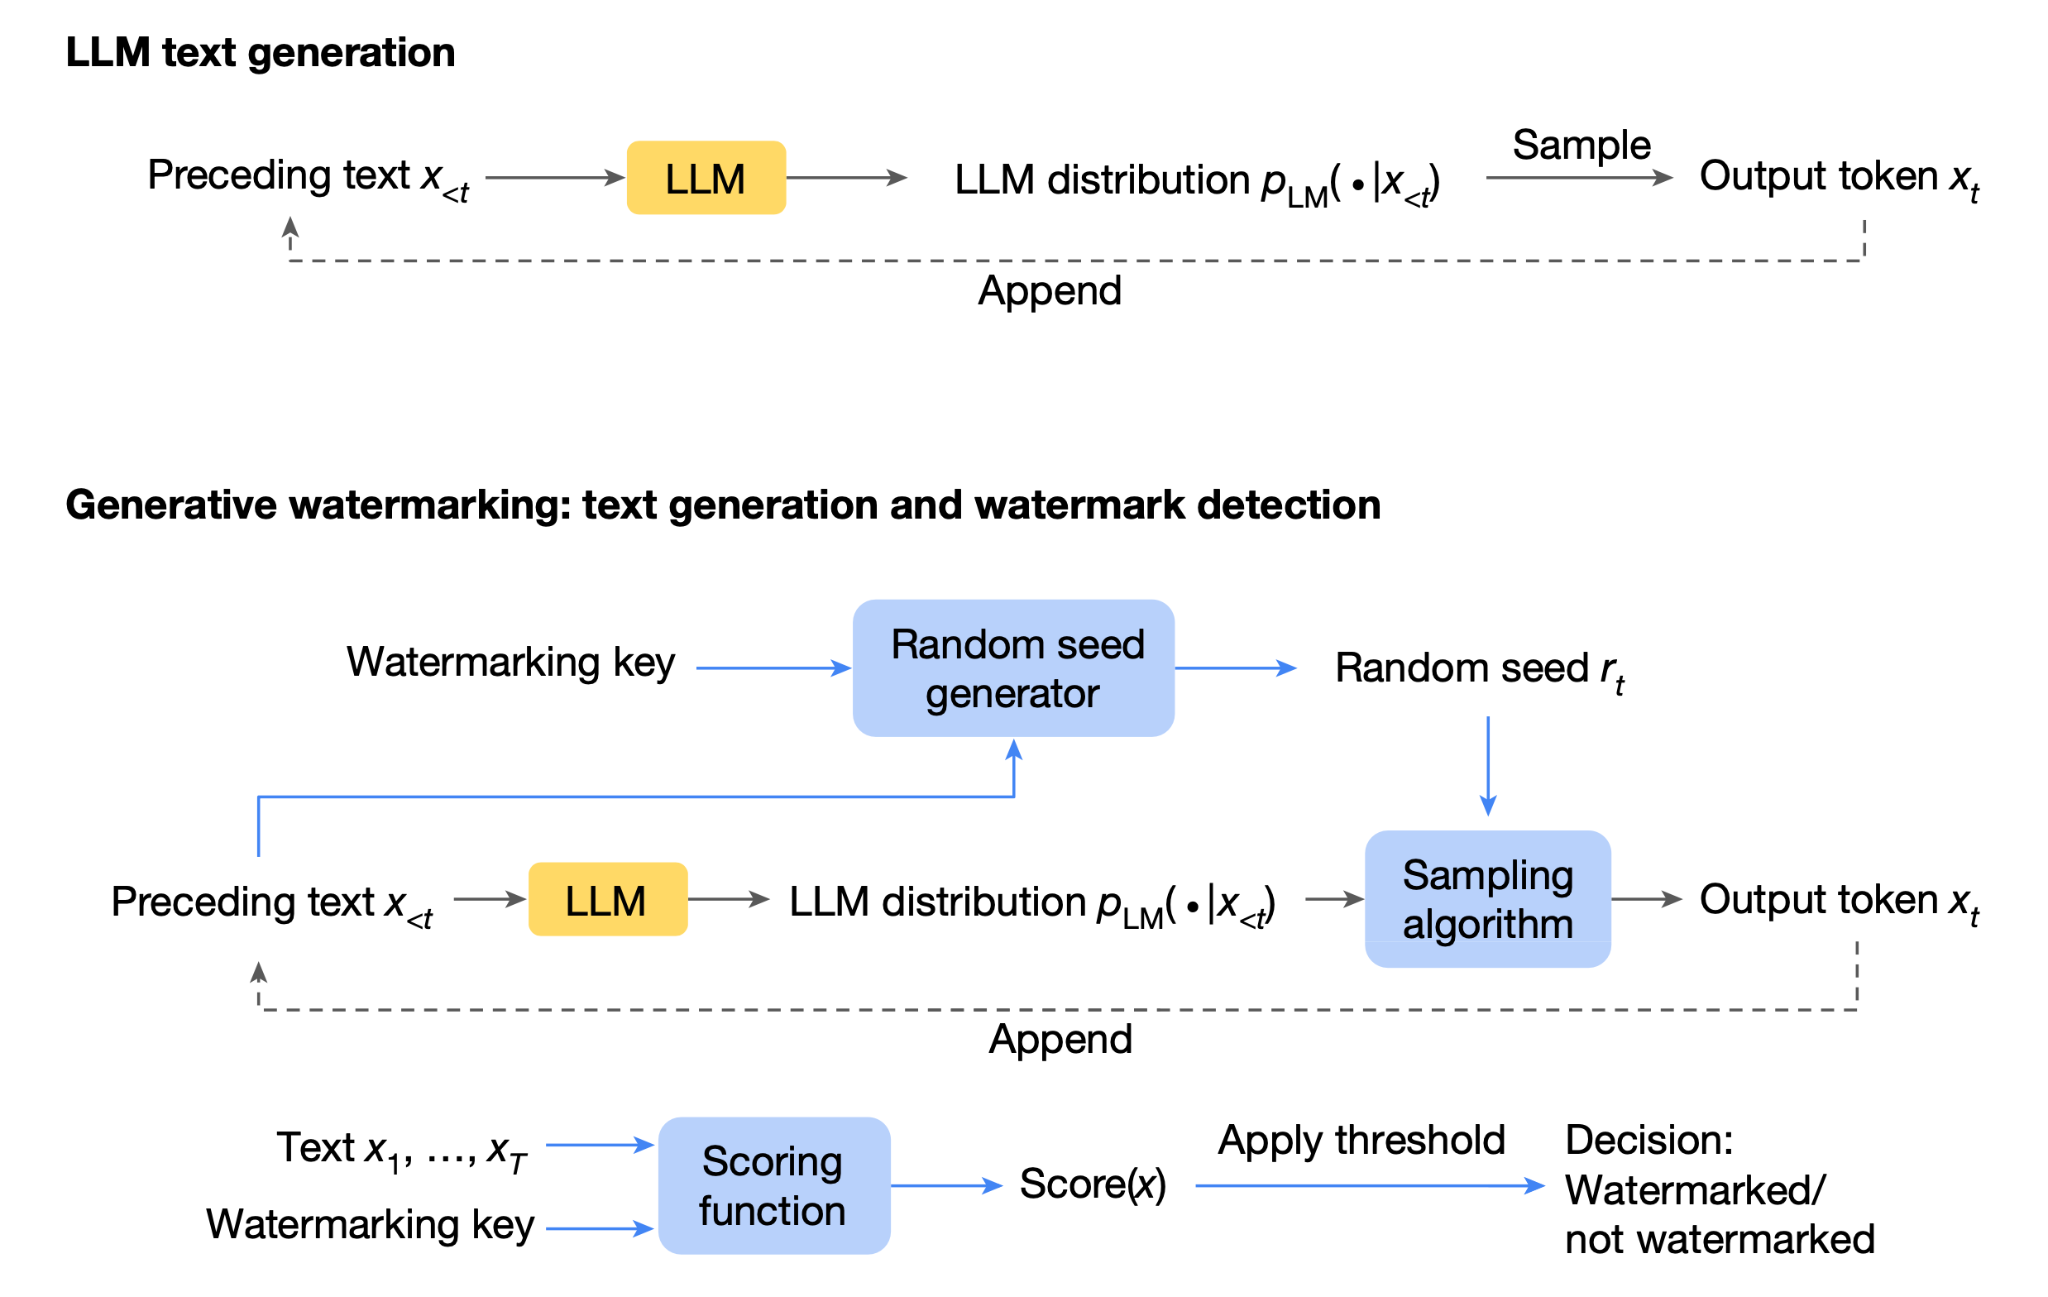
AI watermarks may weaken safety guardrails
New research reveals that watermarking techniques designed to identify AI-generated text can paradoxically make models more vulnerable to harmful prompts.
Ars Technica · 2m

The white-text trick job seekers use on AI screeners
Applicants are hiding instructions in their resumes to talk past the AI that decides who gets read.
PCMAG · 2m · 6 views